
The threat is real. The solution is proven.
What you need
to know.
Four pillars. One standard.The questions serious operators actually ask.
CybersecurityThe standard others follow.
The standard others follow.
We wrote it.
IMO 2021, IASME Maritime Cyber Baseline, incident response, and what real cyber defence actually looks like for maritime operators and private clients.
Maritime Compliance
IMO Resolution MSC-FAL.1/Circ.3 requires vessel operators to integrate cyber risk management into their Safety Management System under the ISM Code. Most providers treat this as a generic template-filling exercise; we do not.
Official certification is granted strictly by flag states and Classification Societies. Our role is to ensure your operations are so thoroughly prepared that the actual audit becomes a mere formality.
For most of the maritime sector, this territory is still entirely new. Traditional maritime advisers rarely understand deep cyber security, while standard tech firms fail to grasp maritime regulation. We are the rare exception that masters both. Because our founders co-authored the IASME Maritime Cyber Baseline, we advise across the entire fragmented matrix. We translate not just the shifting international rules, but the actual technical cyber requirements into a single, cohesive strategy. We bridge the gap between compliance and true defence, ensuring your fleet is both legally bulletproof and genuinely secure.
Connectivity is not security. Your ship manager handles uptime, bandwidth, cables and hardware. They are structured as a utility helpdesk, not a tactical defence unit. The gap between their operational checklist and an active threat is exactly where multi-million-pound crises happen.
CyberPlus doesn't just add a supplementary layer to your ship manager's setup; we provide the overarching strategic guidance, advice and monitoring they need to operate safely. A vessel is not a corporate office block. For critical Operational Technology (OT) networks like propulsion and navigation, maritime regulations are uncompromising. Any application that actively interacts with these systems must clear exhaustive type approvals and class certifications before it is allowed on board. In these sensitive environments, we deploy sophisticated, passive monitoring to track threats safely without triggering accidental shutdowns or regulatory deadlocks.
For non-OT systems, we provide comprehensive active management, embedding advanced capabilities like honeypots and deception networks to trap attackers before they can pivot. We bridge the gap between compliance and technical execution, delivering the proactive, multi-layered defence that a general IT desk is simply not engineered to provide.
The first ten minutes determine whether an exploit remains contained or scales into a total catastrophe. Our response protocols are pre-defined, automated and battle-tested over two decades of critical infrastructure defence.
Detection triggers an immediate, aggressive containment protocol by our SOC. Simultaneously, we arm your team with the secure, out-of-band communication protocols and definitive technical data required to notify your DPA, underwriters and P&I Club without delay. You do not spend the golden hours of a breach figuring out who needs to know what; we provide the clarity required to execute your internal notification checklist instantly. By hour four, containment is finalised and a clear impact brief is delivered. By hour 24, you possess a legally defensible audit trail of the remediation: the exact technical and regulatory standard your insurers demand to honour a claim.
Detection triggers an immediate, aggressive containment protocol by our SOC. Simultaneously, we arm your team with the secure, out-of-band communication protocols and definitive technical data required to notify your DPA, underwriters and P&I Club without delay. You do not spend the golden hours of a breach figuring out who needs to know what; we provide the clarity required to execute your internal notification checklist instantly. By hour four, containment is finalised and a clear impact brief is delivered. By hour 24, you possess a legally defensible audit trail of the remediation: the exact technical and regulatory standard your insurers demand to honour a claim.
No. Most boards confuse basic digital hygiene with true strategic defence. Firewalls and endpoint protection are entry-level requirements; they are checklists, not a strategy. Professional attackers do not run headfirst into firewalls; they exploit the human, vendor and physical boundaries between those checklists.
With more than 20 years of high-stakes security lineage defending critical infrastructure and global corporations, we know exactly how modern threat actors operate. In an industry where deep cyber capability is still rare, choosing to discover the difference between an IT checklist and true defence the hard way means you rarely get a second chance to fix it.
With more than 20 years of high-stakes security lineage defending critical infrastructure and global corporations, we know exactly how modern threat actors operate. In an industry where deep cyber capability is still rare, choosing to discover the difference between an IT checklist and true defence the hard way means you rarely get a second chance to fix it.
Superyacht & Private Clients
The scale of the risk is no less severe, but the nature of the threat is fundamentally different. While commercial vessels are typically targeted for systemic operational disruption, cargo theft or fleet-wide financial ransom, a superyacht is targeted specifically because of the high profile of the principal on board.
On a private vessel, the threat shifts from corporate liability to direct personal vulnerability, where an exploit means targeted physical tracking, guest device compromise and bespoke blackmail. Our superyacht programmes protect the very thing a private vessel is built to provide: total isolation from the outside world. We manage the entire digital perimeter across the full lifecycle of ownership, ensuring that your location, your conversations and your inner circle remain completely invisible to threat actors. We don't just secure the hull; we safeguard the absolute luxury of complete privacy.
On a private vessel, the threat shifts from corporate liability to direct personal vulnerability, where an exploit means targeted physical tracking, guest device compromise and bespoke blackmail. Our superyacht programmes protect the very thing a private vessel is built to provide: total isolation from the outside world. We manage the entire digital perimeter across the full lifecycle of ownership, ensuring that your location, your conversations and your inner circle remain completely invisible to threat actors. We don't just secure the hull; we safeguard the absolute luxury of complete privacy.
Prevention is a continuous operational discipline, not a point-in-time achievement. Powered by over two decades of proprietary intelligence, we actively hunt for vulnerabilities and threat indicators before they can be weaponised against your estate or vessel.
We systematically remove the strategic conditions that make an attack viable or profitable. By the time a standard security team or an internal IT desk receives an automated alert, our architecture has already closed the door the attacker was walking towards.
We systematically remove the strategic conditions that make an attack viable or profitable. By the time a standard security team or an internal IT desk receives an automated alert, our architecture has already closed the door the attacker was walking towards.
We wrote the standard the rest of the maritime industry is trying to navigate. The founders of CyberPlus were the principal architects of the IASME Maritime Cyber Baseline: the framework that now governs maritime cyber risk management internationally.
For over twenty years, our analysts have operated in high-consequence environments where the stakes are measured in asset survival and human safety. We do not require an industry primer, an onboarding period or environment orientation. We bridge the gap between complex cyber-physical spaces and international maritime regulation because we helped define the terms.
For over twenty years, our analysts have operated in high-consequence environments where the stakes are measured in asset survival and human safety. We do not require an industry primer, an onboarding period or environment orientation. We bridge the gap between complex cyber-physical spaces and international maritime regulation because we helped define the terms.
True readiness has nothing to do with basic compliance videos or ticking a box for annual security hygiene training. It is the absolute distinction between a contained technical anomaly and a total operational catastrophe.
We replace passive awareness with operational muscle memory. True readiness means designing rigorous, vessel-specific incident response workflows and continuously stress-testing them through live practical drills. We don't just check if your crew can spot a phishing email; we test their workflow knowledge under pressure so they know exactly what to do, and who to contact, the moment a system goes dark. When a real threat materialises, panic is entirely eliminated because calculated tactical action is already in motion.
We replace passive awareness with operational muscle memory. True readiness means designing rigorous, vessel-specific incident response workflows and continuously stress-testing them through live practical drills. We don't just check if your crew can spot a phishing email; we test their workflow knowledge under pressure so they know exactly what to do, and who to contact, the moment a system goes dark. When a real threat materialises, panic is entirely eliminated because calculated tactical action is already in motion.
Remote AccessSovereign access.
Sovereign access.
Audited to the session.
As TeamViewer's first global MSP, we govern secure remote access for the world's most demanding operational environments, from vessel control systems to UHNW estates.
Governance & Control
No one has access to your systems without an explicit, permissioned session and every session is recorded, timestamped, and attributed to a named individual. This is not a policy statement; it is an architectural reality.
As TeamViewer's first global MSP, we implement access controls to enterprise governance standards: role-based permissions, session duration limits, and a complete audit log that satisfies both your legal team and your insurer. For UHNW principals and their advisors, that log is available on demand. Sovereignty over your own infrastructure is not negotiable.
As TeamViewer's first global MSP, we implement access controls to enterprise governance standards: role-based permissions, session duration limits, and a complete audit log that satisfies both your legal team and your insurer. For UHNW principals and their advisors, that log is available on demand. Sovereignty over your own infrastructure is not negotiable.
Standard resellers distribute licences. We were appointed TeamViewer's first global Managed Service Provider, a distinction that means we design, secure, and operate the access architecture rather than hand you software and leave.
That appointment reflects a specific capability: the ability to deploy TeamViewer into high-stakes, security-critical environments and govern it to the standard those environments demand. On a vessel, an offshore installation, or an estate with distributed infrastructure, that difference matters.
In Mark Oakton's words at the official launch: "Cybersecurity is the foundation of the trust we build with our clients, protecting their business while unlocking new efficiencies and a competitive edge. Our partnership with TeamViewer strengthens that trust, combining cyber expertise with AI, AR, DEX, and remote monitoring and management of IT, OT, and IoT systems."
Read the TeamViewer announcement
While TeamViewer provides industry-leading connectivity, ungoverned remote access is a primary vector for cyber attacks. Many organisations unknowingly suffer from shadow IT deployments of standard remote tools that bypass security protocols entirely.
As TeamViewer's first global managed service partner, CyberPlus wraps your existing estate in Zero Trust governance. Utilising TeamViewer One for centralised visibility alongside TeamViewer Tensor, we implement role-based access control, conditional access, and full session auditing. We take over management without a disruptive rip-and-replace process, turning an unmonitored risk into a secure, compliant asset.
As TeamViewer's first global managed service partner, CyberPlus wraps your existing estate in Zero Trust governance. Utilising TeamViewer One for centralised visibility alongside TeamViewer Tensor, we implement role-based access control, conditional access, and full session auditing. We take over management without a disruptive rip-and-replace process, turning an unmonitored risk into a secure, compliant asset.
Regulators and insurers across every sector no longer accept unmonitored third-party or employee access as a manageable risk. Whether your obligations sit under NIS2, ISO 27001, IMO 2021, Cyber Essentials Plus, or the requirements of your specific P&I Club or underwriter, the fundamental demand is the same: you must demonstrate exactly who accessed your network, when they did so, and what actions they performed.
Our managed TeamViewer Tensor deployments provide enterprise-grade audit trails, end-to-end 256-bit AES encryption, and comprehensive session logging. This delivers the legally defensible proof of control that auditors require, ensuring your remote connectivity actively supports your compliance posture rather than threatening it. For clients in maritime, energy, legal, or financial environments, that audit trail also becomes your first line of defence in the event of an insurance claim or regulatory investigation.
Our managed TeamViewer Tensor deployments provide enterprise-grade audit trails, end-to-end 256-bit AES encryption, and comprehensive session logging. This delivers the legally defensible proof of control that auditors require, ensuring your remote connectivity actively supports your compliance posture rather than threatening it. For clients in maritime, energy, legal, or financial environments, that audit trail also becomes your first line of defence in the event of an insurance claim or regulatory investigation.
Yes. TeamViewer is our governance platform of choice because of the depth of control and auditability it provides, and because no other vendor offers the same combination of enterprise security capability and operational reliability across maritime and distributed environments.
If you are currently running a different remote access tool, we conduct an access audit of your existing estate, identify the governance gaps, and migrate you to a managed TeamViewer architecture without operational disruption. The starting point is your current risk exposure, not your current software licence.
If you are currently running a different remote access tool, we conduct an access audit of your existing estate, identify the governance gaps, and migrate you to a managed TeamViewer architecture without operational disruption. The starting point is your current risk exposure, not your current software licence.
Our SOC detects anomalous session behaviour in real time. If a session triggers a policy violation or displays indicators of compromise, access is suspended automatically while our analysts investigate. You are notified immediately with a plain-language brief: what happened, what was contained, and what remediation is underway.
Because every session is logged and attributed through TeamViewer Tensor, we can provide your legal team, insurers, and any regulatory body with a complete, timestamped account of the incident from first access attempt to resolution. In the event of a claim, that audit trail is the difference between a covered incident and a disputed one.
Because every session is logged and attributed through TeamViewer Tensor, we can provide your legal team, insurers, and any regulatory body with a complete, timestamped account of the incident from first access attempt to resolution. In the event of a claim, that audit trail is the difference between a covered incident and a disputed one.
Operational Use Cases
We layer on top. CyberPlus does not require you to change your existing IT arrangements; we integrate with them, closing the governance gaps that general IT providers are not equipped to address.
In practice, your existing provider continues handling day-to-day infrastructure. We govern the security overlay: remote access permissions, threat monitoring, incident response, and compliance posture. Most clients find that their IT provider welcomes the delineation.
In practice, your existing provider continues handling day-to-day infrastructure. We govern the security overlay: remote access permissions, threat monitoring, incident response, and compliance posture. Most clients find that their IT provider welcomes the delineation.
Offshore and maritime environments are precisely where standard remote access solutions fail. We have built deployment configurations that operate reliably across VSAT, 4G, and hybrid satellite connections, including graceful degradation protocols that maintain audit integrity even when bandwidth drops significantly.
Our VISION+ platform was designed with these constraints as first principles, not afterthoughts. Remote expert intervention does not require a stable broadband connection; it requires the right architecture.
Our VISION+ platform was designed with these constraints as first principles, not afterthoughts. Remote expert intervention does not require a stable broadband connection; it requires the right architecture.
Unrestricted access is never safe, but secure, segmented access is essential for modern fleet operations. Original Equipment Manufacturers (OEMs) and vendors frequently require access to OT systems for diagnostics and maintenance, and refusing that access entirely is not a viable operational position.
Through TeamViewer Tensor, we establish highly restricted, monitored "just-in-time" access. Vendors are granted access only to the specific machinery they need to service, for a defined time window, with every action logged and monitored by our cybersecurity team. This protects the wider vessel network while significantly reducing costly physical dispatch fees.
Through TeamViewer Tensor, we establish highly restricted, monitored "just-in-time" access. Vendors are granted access only to the specific machinery they need to service, for a defined time window, with every action logged and monitored by our cybersecurity team. This protects the wider vessel network while significantly reducing costly physical dispatch fees.
Onboarding & Commercial
Standard remote support is entirely reactive. IT teams wait for a system to fail, a user to raise a complaint, or a vessel to report an outage before connecting to investigate.
TeamViewer DEX, managed by CyberPlus, shifts your operations from reactive troubleshooting to proactive maintenance. DEX provides continuous telemetry and device intelligence, allowing our team to identify CPU bottlenecks, network degradation, or software crashes before they impact your crew or operations. For mission-critical assets, the difference between detecting a problem at 2am and being called about it at 6am is not cosmetic. It is the difference between a contained anomaly and a full operational outage.
TeamViewer DEX, managed by CyberPlus, shifts your operations from reactive troubleshooting to proactive maintenance. DEX provides continuous telemetry and device intelligence, allowing our team to identify CPU bottlenecks, network degradation, or software crashes before they impact your crew or operations. For mission-critical assets, the difference between detecting a problem at 2am and being called about it at 6am is not cosmetic. It is the difference between a contained anomaly and a full operational outage.
Pricing is structured around your estate: the number of managed devices, the complexity of access roles required, and the level of monitoring and incident response you need. We do not publish a rate card because a superyacht with four vendor relationships and a fleet operator managing forty vessels are not the same problem. Every engagement begins with a scoping conversation.
Onboarding typically follows a three-phase process: access audit and credential inventory, governance framework deployment via TeamViewer One and Tensor, and handover to active managed monitoring. For most clients, this is completed without any interruption to existing operations. The goal is that your team notices the governance, not the transition.
Onboarding typically follows a three-phase process: access audit and credential inventory, governance framework deployment via TeamViewer One and Tensor, and handover to active managed monitoring. For most clients, this is completed without any interruption to existing operations. The goal is that your team notices the governance, not the transition.
VISION+Secure control.
Secure control.
Intelligence everywhere.
Live visual collaboration, interactive digital workflows, automated compliance, and real-time business intelligence built on absolute cyber security.
About VISION+
It is intelligent secure remote collaboration and control.
Multiplies Scarce Expertise: It solves the operational strain of distributed teams, shrinking workforces, and ageing expertise by linking your remote or off-shore team instantly to shore-based specialists. A single expert can visually guide multiple crews through complex tasks simultaneously, ensuring critical operational knowledge is shared across the business before it retires. It also stops external stakeholders, clients, and project managers from having to fly out to remote sites or shipyards all the time, allowing them to collaborate and inspect progress live with complete clarity.
Multiplies Scarce Expertise: It solves the operational strain of distributed teams, shrinking workforces, and ageing expertise by linking your remote or off-shore team instantly to shore-based specialists. A single expert can visually guide multiple crews through complex tasks simultaneously, ensuring critical operational knowledge is shared across the business before it retires. It also stops external stakeholders, clients, and project managers from having to fly out to remote sites or shipyards all the time, allowing them to collaborate and inspect progress live with complete clarity.
No. Unlike standard collaboration tools that patch security on as an afterthought, VISION+ is built by cybersecurity experts as a hardened infrastructure layer. It encapsulates your remote sessions, workflows, and edge devices within a continuous threat defence fabric, ensuring your operational network remains completely insulated from external risk.
Built by the founders of Infosec Partners, CyberPlus is the evolution of a 20-year track record in high-stakes security. In 2025, TeamViewer appointed us as their first global MSP: a milestone that validates our ability to apply proven intelligence to the world's most demanding environments.
Capability
It gives off-site specialists secure, direct control over IT-connected systems to perform complex tests and configurations whilst local operators observe. Simultaneously, it converts static manuals into interactive, step-by-step digital workflows that technicians follow via smart glasses or apps, ensuring jobs are executed safely and flawlessly without senior staff needing to travel.
It automates them entirely. Instead of relying on manual paperwork after a job is completed, VISION+ converts active frontline data into instant, structured reports and unalterable digital audit trails in real time. Headquarters gets immediate operational intelligence and automated compliance documentation without the wait.
Standard MSPs are software resellers without operational engineering experience. We are elite cybersecurity and operational infrastructure specialists. We do not just hand you a licence; we integrate your entire remote support ecosystem, bake threat defence into the architecture, and actively protect your high-stakes operations.
Commercial Workflow
Yes. An inspection triggers an immediate commercial workflow. On-site staff identify replacement parts through the interface, and this data allows the platform to generate accurate quotes instantly, reducing the lead time between fault detection and resolution from days to minutes.
The hardware is just the delivery mechanism. VISION+ runs seamlessly across certified smart glasses, smartphones, drones, and ROVs, but the real core is the intelligence platform behind them. We specify the right device for your specific environment, then link it directly to the real-time data, AI workflows, and cyber security that actually make the hardware smart.
We do not define our reach by sector, but by the stakes of the operation. If your organisation relies on distributed teams, high-consequence technical tasks, strict compliance, or critical network security, the platform is built for you. Operational headaches like talent shortages, mounting travel costs, human error, and cyber risk do not care about industry labels.
Eyes-OnWhere cyber
Where cyber
meets physical.
Smart-glass-enabled surveillance, executive protection, and maritime security for principals who require more than CCTV.
What Eyes-On Is
CCTV records. Eyes-On acts. Our cyber-physical convergence platform equips security personnel with smart glasses that stream live visual data to a remote command centre, enabling real-time expert guidance, anomaly flagging, and coordinated response rather than passive recording.
For a superyacht owner or UHNW principal, that distinction matters because the threat landscape they face combines digital and physical vectors simultaneously. A vessel intrusion, a credential-based access attempt, a compromised vendor device: Eyes-On is designed to identify and respond to all three as a unified security event.
For a superyacht owner or UHNW principal, that distinction matters because the threat landscape they face combines digital and physical vectors simultaneously. A vessel intrusion, a credential-based access attempt, a compromised vendor device: Eyes-On is designed to identify and respond to all three as a unified security event.
Deck crew or security personnel wear the smart glass unit during harbour approaches, port calls, and charter turnarounds, the highest-risk periods for physical access and social engineering. Their field of view is live-monitored by a remote CyberPlus specialist who can identify anomalies, confirm identities, and direct the on-vessel team in real time.
All footage is encrypted, timestamped, and stored in a defensible audit trail that protects both the principal and the operator in the event of an incident or insurance claim.
All footage is encrypted, timestamped, and stored in a defensible audit trail that protects both the principal and the operator in the event of an incident or insurance claim.
Executive & Estate Use
Yes. Eyes-On was designed for any environment where a principal's physical security intersects with digital access risk. Event security, estate perimeter monitoring, and close protection operations all benefit from the same live-stream command capability, with the additional layer that a CyberPlus specialist can simultaneously monitor for cyber-side threats that a conventional security team would not detect.
For family offices managing principal security across multiple locations, Eyes-On provides a unified operational picture rather than disconnected site-by-site reports.
For family offices managing principal security across multiple locations, Eyes-On provides a unified operational picture rather than disconnected site-by-site reports.
Every session is end-to-end encrypted, stored on infrastructure that the principal's legal team can specify, and governed by a data handling agreement we produce before deployment.
Access to footage is role-permissioned and logged. For UHNW principals and their advisors, data sovereignty is non-negotiable: footage of a principal's movements, guests, or security posture must never leave a controlled environment. We architect that control before the first session begins.
Access to footage is role-permissioned and logged. For UHNW principals and their advisors, data sovereignty is non-negotiable: footage of a principal's movements, guests, or security posture must never leave a controlled environment. We architect that control before the first session begins.
Case Scenarios
These answer the why.
Four environments. The same standard of resolution.
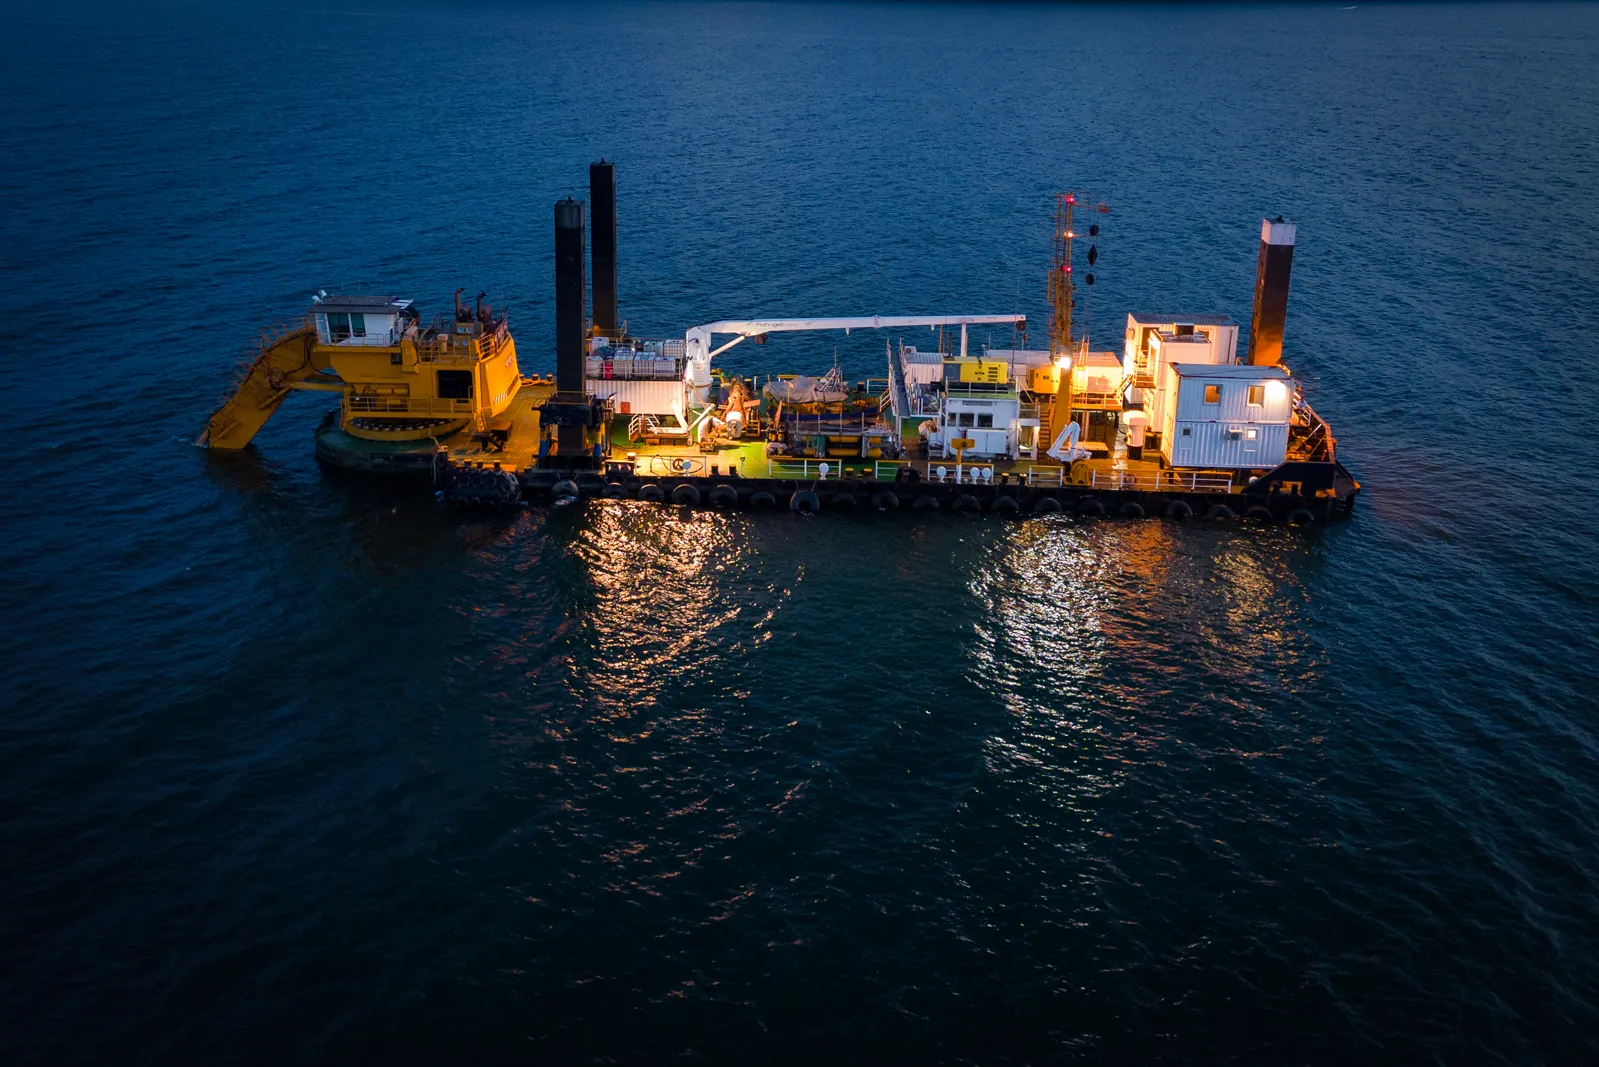
Deep-Sea Equipment
Deep-Sea EquipmentThe 3am Lie
The call comes in at 3am. A contractor, standing on a vessel offshore in a different time zone, tells the support engineer that the equipment is dead. He has checked everything, he says.
He hasn't. Admitting an oversight in front of his crew is not something he is willing to do. So here they are: the meter running at £50,000 an hour, neither man able to move without losing something.
Twenty minutes later, the engineer knows. This is not a technical problem.
The New Standard
Proof by default.
- Hands-free guided workflowsStep-by-step verification on headset. The process does the work, not the conversation.
- Timestamped data captureEvery check recorded automatically. The facts are established before the conversation begins.
- You see what I seeThe engineer sees exactly what the contractor sees. Expertise delivered without a flight booking.
Commercial Maritime
Commercial MaritimeThe 35 Year Exit
He has thirty-five years of knowing exactly what a P&I Club needs to see to approve a risk. That instinct exists nowhere except inside his head.
The average age of a maritime inspector is rising towards retirement. When they go, they do not take a checklist with them. They take the ability to spot a liability before it becomes a claim.
The Resolution
"He retired in June. He still reviews 12 P&I inspections a month from his kitchen table in Lisbon."
- Institutional risk captureBest-practice workflows built against specific P&I Club requirements. Junior staff capture exactly what insurers need.
- Remote mentorshipSeniors remain high-value consultants. Juniors are the hands. The expert provides final remote verification.
- Defensible audit trailEvery inspection recorded and timestamped. Institutional memory that outlasts any individual career.
Superyacht
SuperyachtThe Quiet Vessel
The captain ran a tight ship. Every system had a procedure. Every vendor had a contract. When the owner's schedule appeared on a charter broker's website six weeks before it was announced, no one understood how.
The vessel had not been hacked in any conventional sense. A former crew member still had active credentials to a navigation system connected to the guest WiFi during a refit three years earlier. No one had revoked them when he left.
The vessel was perfectly maintained. It was completely silent about everything it knew.
The New Standard
"We didn't find a breach. We found seventeen doors that had never been closed."
- Credential lifecycle managementEvery access credential is tied to a named individual and a defined role. When the role ends, the access ends automatically.
- Network segmentation auditGuest, crew, operational, and navigation networks are verified as isolated. Not assumed to be.
- AIS and schedule privacyVessel broadcast settings and third-party data exposure are reviewed against the principal's privacy requirements. A defined protocol, not an afterthought.
UHNW Estate
UHNW EstateThe Vendor Key
The estate's IT was exemplary by every conventional measure. Cyber Essentials certified. The IT provider was responsive, professional, and well-regarded. The principal's family office was satisfied.
What no one had reviewed was the remote access credentials issued to the building management vendor during a smart-home installation two years earlier. The vendor had sub-contracted the job. The sub-contractor had since changed ownership. Three people who had never met the principal now had remote access to the estate network.
The Resolution
"The IT provider had done everything right. No one had asked the right questions."
- Third-party access governanceEvery vendor credential is inventoried, permissioned to a defined scope, and subject to periodic re-authorisation. Sub-contractors inherit no access by default.
- Session audit logAll remote access sessions are recorded and attributed. The principal's legal team can request the full audit trail at any time.
- Cyber-physical integrationSmart-home, AV, and building management systems are treated as part of the security architecture. Eyes-On monitoring covers the physical access layer simultaneously.