
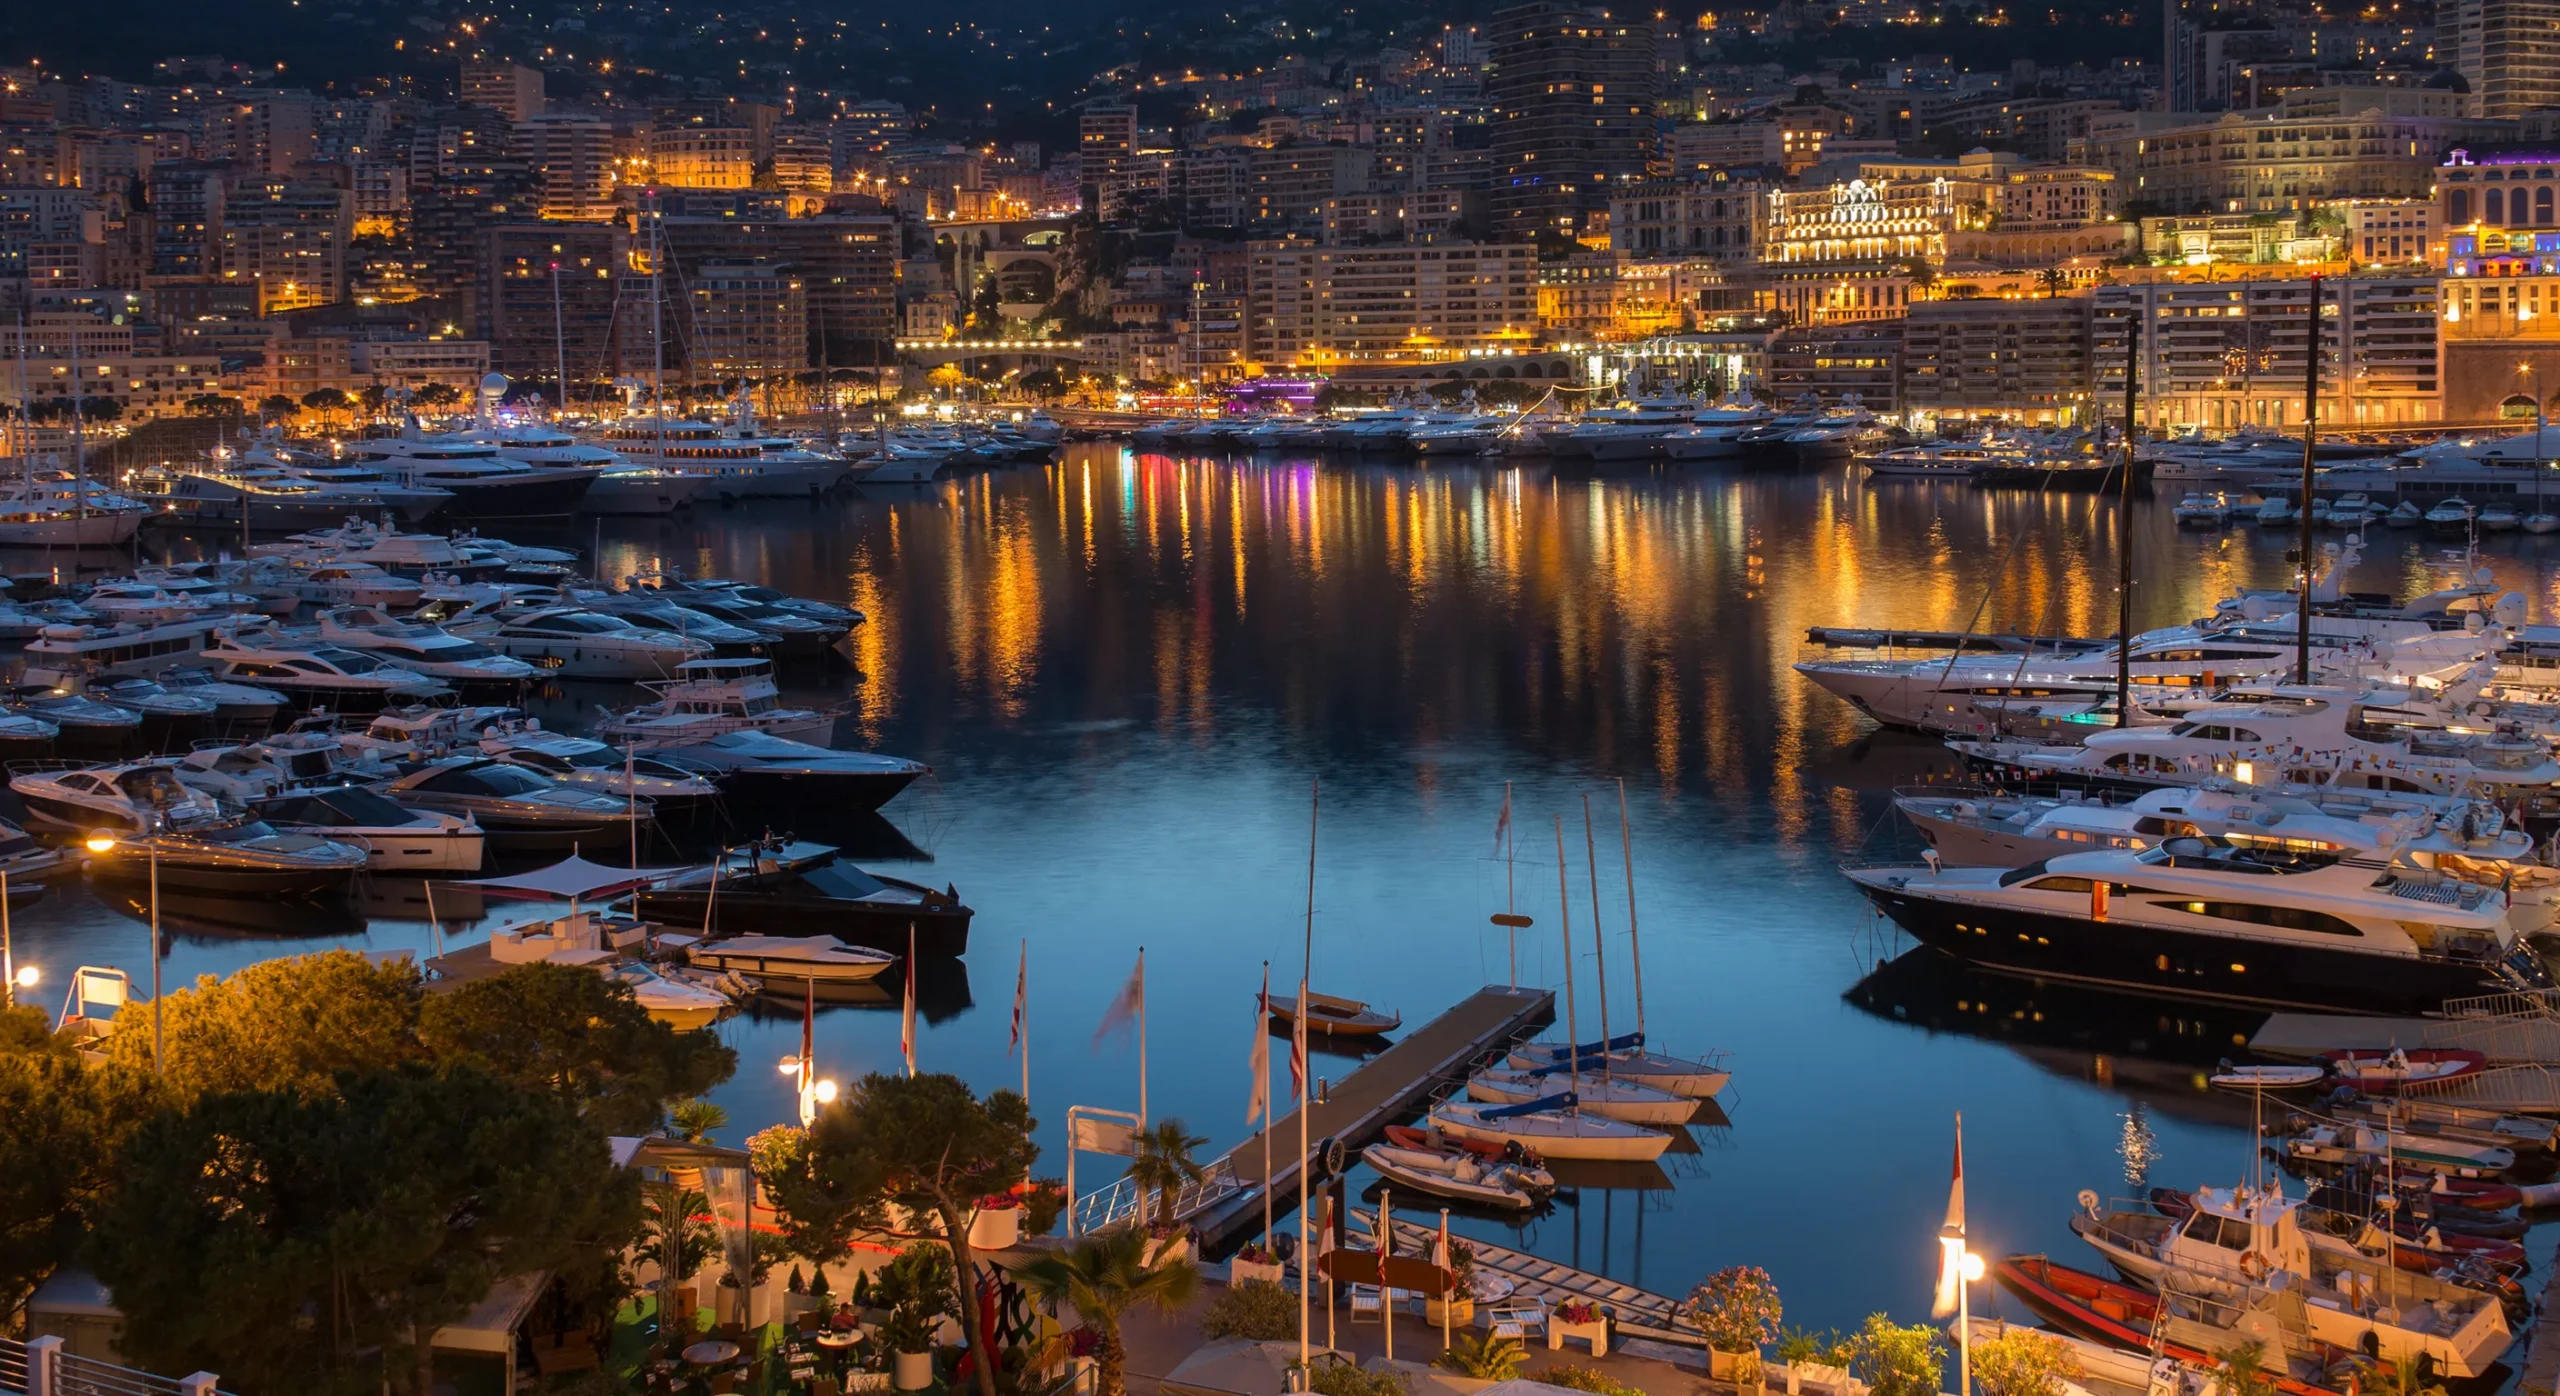
Everything's discreet. Except for the Wi-Fi. Name it "Owner", and everyone knows where to find you
Superyacht security is traditionally measured in bulk: reinforced glass, anti-paparazzi acoustics, trained former-special-forces crew, and encrypted satellite uplinks. Yet sitting quietly inside the wheelhouse is a tiny, zero-cost oversight that quietly dismantles every physical precaution taken on deck.
Every Wi-Fi access point advertises its presence by broadcasting beacon frames many times per second in plain text. Anyone within radio range on the quay or a neighbouring berth can read that broadcast without authenticating or connecting. When a vessel configures its wireless networks around standard sector naming conventions, such as "M/Y [Vessel] Owner", "... Captain", or "... Guest", it turns a convenience label into an unencrypted digital beacon.
Physical privacy and cyber vulnerability converge at this exact seam. Superyacht owners invest heavily to obscure their movements, yet a broadcast network containing the vessel's name provides a real-time digital confirmation that answers two key operational questions: exactly which vessel is berthed here, and which high-value networks are active.
Evidence from open databases: The Port Hercule study
This is not a theoretical vulnerability. To measure the practical scope of network naming habits in the maritime sector, CyberPlus executed a narrow open-source intelligence (OSINT) audit over a single geographic slice: Port Hercule, Monaco.
Using a single free, public wardriving database (WiGLE.net) and filtering strictly for one vessel prefix ("M/Y"), the audit uncovered 45 distinctly named motor yachts broadcasting approximately 300 unique access points in clear text. Role segmentation by name was widespread.
The most exposed vessel alone broadcast 125 distinct access points cleanly segmented into "Owner", "Crew", "Crew Office", "Guest", "A/V", and "WAM" networks. A second vessel exposed 67 access points across five role-labelled names. Because volunteers log these networks globally using GPS-tagged receivers, historical data allows remote analysts to reconstruct seasonal patterns of movement across ports spanning more than a decade without ever visiting a marina.
"Tinted glass protects your privacy on deck. A poorly named Wi-Fi network surrenders it across the harbour."
Three technical myths that increase exposure
Hiding an SSID removes the name from access point beacons, but forces client devices to actively search for it. When an owner's phone saves a hidden network, it broadcasts directed probe requests carrying the vessel's full name wherever the phone goes, including when the principal is in a hotel, restaurant, or airport miles inland. Hiding the network relocates the leak from the harbour directly into the owner's pocket.
Modern iOS and Android devices randomise their hardware MAC addresses to frustrate physical tracking. While this protects the phone's individual identity, it does nothing to obscure the broadcast name (SSID) of the network itself. The network name remains fully visible to passive receivers regardless of client privacy settings.
Open guest networks featuring captive sign-in portals manage access, but leave all over-the-air traffic completely unencrypted. Nearby observers can passively sniff data frames in clear text while the portal database creates a centralised, loggable map binding real guest identities to device addresses and cabin locations.
Remediation: Discretion costs nothing
Correcting network exposure requires no hardware overhauls or expensive subscription software. The solution is pure operational discretion.
First, strip all vessel names, owner references, and functional roles from broadcast SSIDs. Internal network segmentation should be retained for security, but public labels should be replaced with neutral identifiers (e.g. NET-A, NET-B).
Second, replace shared pre-shared keys (WPA2 passwords) and MAC allow-lists with identity-based 802.1X/EAP-TLS authentication. Issuing client certificates via Mobile Device Management (MDM) allows seamless connection for trusted principal devices while allowing MAC randomisation to stay fully enabled without breaking network access.
"Comprehensive risk management leaves no gap between physical discretion on deck and technical exposure on the airwaves."
Three questions for captains and family offices
Evaluating whether your vessel or fleet is currently exposed requires zero technical background. Three questions highlight the gap.
- Does your onboard Wi-Fi broadcast the vessel’s name or reveal internal roles like "Owner", "Captain", or "Guest"?
- Are your principal’s personal devices configured to auto-join a hidden network that forces them to probe for the vessel's name while ashore?
- Has your ETO or integrator searched public wardriving repositories (such as WiGLE or beaconDB) to see if your vessel's past berth locations are archived online?
If any answer reveals an active vessel name on the air, that broadcast is an unmonitored intelligence feed available to anyone within radio range.
At CyberPlus, we work with vessel owners, captains, and family offices to bridge the gap between physical discretion and technical cyber exposure.
Our maritime advisory and risk assessment programmes evaluate technical infrastructure, satellite connectivity, and wireless exposure against real-world intelligence capabilities.
If you would like to audit your fleet's digital footprint, you know where we are.
A vessel's physical perimeter stops intruders at the gangway. A neutral wireless perimeter stops them from ever tracking you.